One place for every finding, and everything that happens to it.
Every agent reports into the same platform: one queue, one severity scale, one report. Run it hosted, or inside your own cloud with the models you choose.
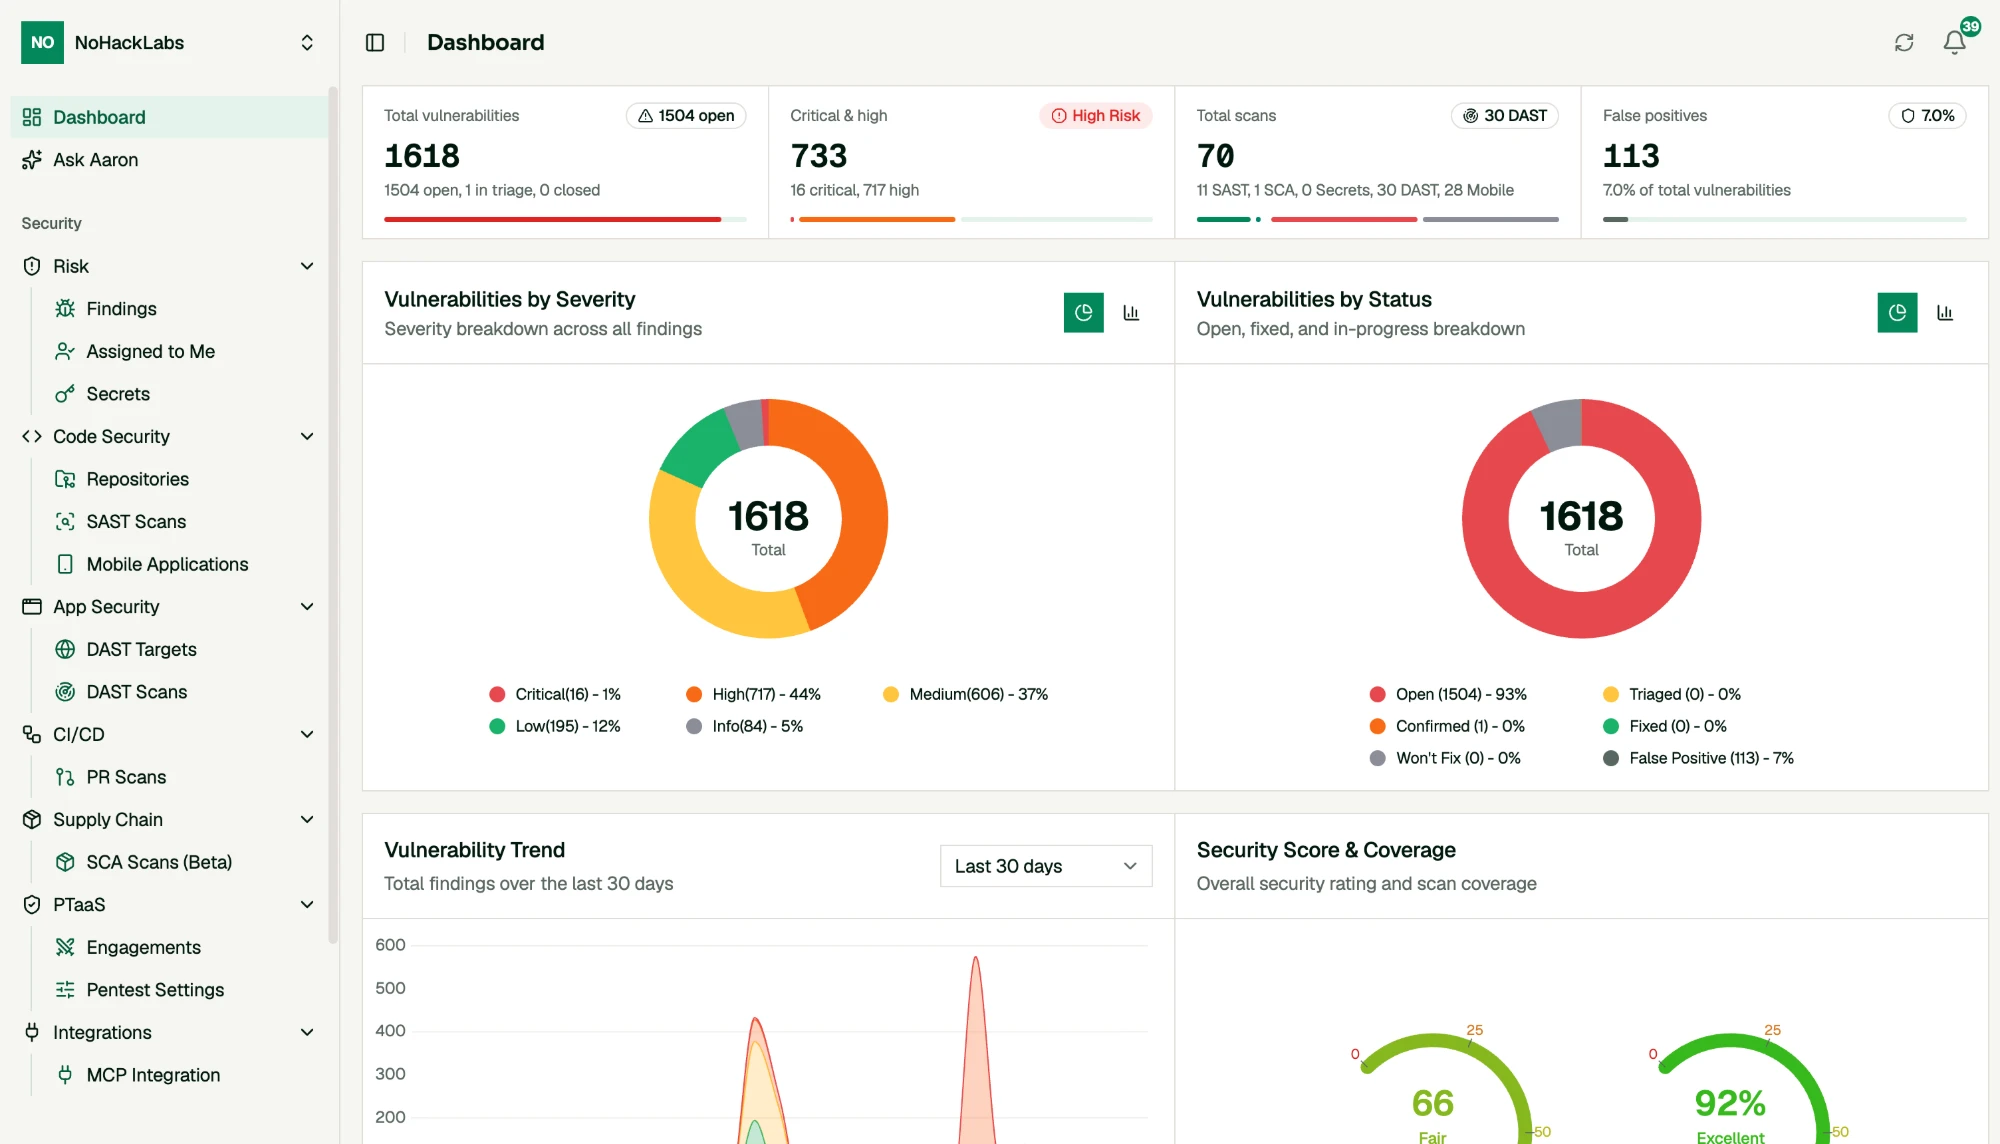
Work the findings.
From the first triage pass to the signed report.
Triage across agents
Code, web, mobile, dependency, and secret findings in one queue. Bulk-triage, assign, override severity, and keep verdicts across audits.
Retest and re-triage
Ask for a retest after a fix (fixed, still present, or uncertain), or a fresh look at a finding with new context.
Aaron, your security agent
One chat across every audit, a chat beside each finding, and a chat inside each indexed codebase. Patches, executive summaries, saved threads.
MCP server
Scans, findings, secrets, and repositories as tools in Claude Desktop, Cursor, and VS Code, for developers in the editor and security teams across every repository.
Pentest engagements
Black-, grey-, or white-box engagements with scope, targets, and methodology. AI white-box engagements start a deep audit at once; finalizing freezes the findings.
GitHub integration
A guided setup registers your own GitHub App on github.com, Enterprise Cloud, or Enterprise Server. Private repos, PR comments, checks, and continuous audits on push.
Share a report
A read-only link to a finished scan for someone outside the platform. Off until an admin allows it, revocable at any time, every view audit-logged.
Reports
DOCX from a standard template or your own, with reproduction steps and evidence. SARIF, CSV, and CycloneDX SBOM exports. Import findings from CSV or Excel.
Control what it touches.
Access, identity, models, and spend. Set by you, enforced by the platform.
Roles and permissions
Owner, admin, member, and viewer, plus custom roles, enforced on every request.
Enforced MFA
TOTP multi-factor authentication, which an organisation can require for every member.
Audit log
A record of who did what, and when, across your organisation.
Tenant isolation
Organisations are isolated at the token, the route, and the database membership.
Any model
Model-agnostic: any provider, or a model you host, through an OpenAI-compatible gateway you control, with a model chosen per agent.
Cost and budgets
Cost per audit and per agent, cache-aware, with Excel export. Monthly and per-audit budgets that track, warn, or pause at the limit.
Deploy it your way.
Same platform, same agents. The difference is whose account it runs in.
Hosted
- Nothing to run or patch
- GitHub App, git URL, or zip upload
- Start with a single repository
Self-hosted
- Any cloud or on-prem: AWS, Azure, GCP, or your data centre
- Kubernetes via Helm, or Docker Compose
- Code and findings stay in your environment; models via your own gateway
Integrations today: GitHub App, git URL and zip upload, outbound webhooks, and the MCP server.
Security at the speed you ship.
Bring a repository, a web app, or an APK. We will walk you through a real audit of it.